Secure Application Engineering
Enterprise Application Engineering

Secure Software Development Services

Enterprise Application Engineering

Build security into every application architecture and delivery lifecycle.

FutureSoft helps you identify threats, design security controls, develop secure software, and validate applications before production while aligning privacy and compliance requirements with the real system and its data flows.

Security Application Development Scope

  • Threat modeling and architecture review
  • Trust boundaries and abuse-case analysis
  • Identity, authentication, and authorization design
  • Role-based and privileged access controls
  • Session and API security
  • Data classification and encryption
  • Secure coding standards
  • Dependency and software supply chain controls
  • SAST, DAST, and SCA coordination
  • Container and image scanning where applicable
  • Logging, audit, and security monitoring
  • Privacy engineering and data retention
  • VAPT remediation and retesting

Secure Delivery Lifecycle

  • Classify application data and identify threat actors, abuse cases, and trust boundaries.
  • Translate business, regulatory, and client policy obligations into security requirements.
  • Review architecture, identity, access, data flows, and integration boundaries.
  • Implement security controls alongside functional development.
  • Automate code, dependency, and configuration checks in CI/CD where supported.
  • Test the application, APIs, and infrastructure-facing interfaces according to scope.
  • Remediate findings and retest critical issues.
  • Produce required evidence, runbooks, and operational handover documentation.

Identify and Access

Enterprise application security starts with knowing who can do what, under which conditions, and how that access is audited. FutureSoft can implement authentication, federation and SSO integration, role-based access, step-up controls where required, session management, and privileged actions in coordination with the client's identity environment.

Data Protection and Privacy

Security controls should follow the data. Application design should classify sensitive information, minimize unnecessary collection, encrypt data in transit and at rest as appropriate, protect secrets, define retention and deletion behavior, and make access and changes auditable.

Compliance Positioning

FutureSoft can engineer controls that support requirements associated with frameworks and laws such as GDPR, India's DPDP Act, PCI DSS, and applicable client policies. The website should not imply that software delivery alone certifies an organization as compliant. Compliance depends on the broader operating environment, governance, policies, and independent assessment.

Deliverables

  • Threat model and architecture findings
  • Security requirements and control matrix
  • Identity and access design
  • Data protection recommendations
  • Secure coding and dependency requirements
  • Automated security gate configuration where scoped
  • VAPT remediation tracker and retest evidence
  • Security handover and operational recommendations

What Can Secure Application Development Services Protect?

01

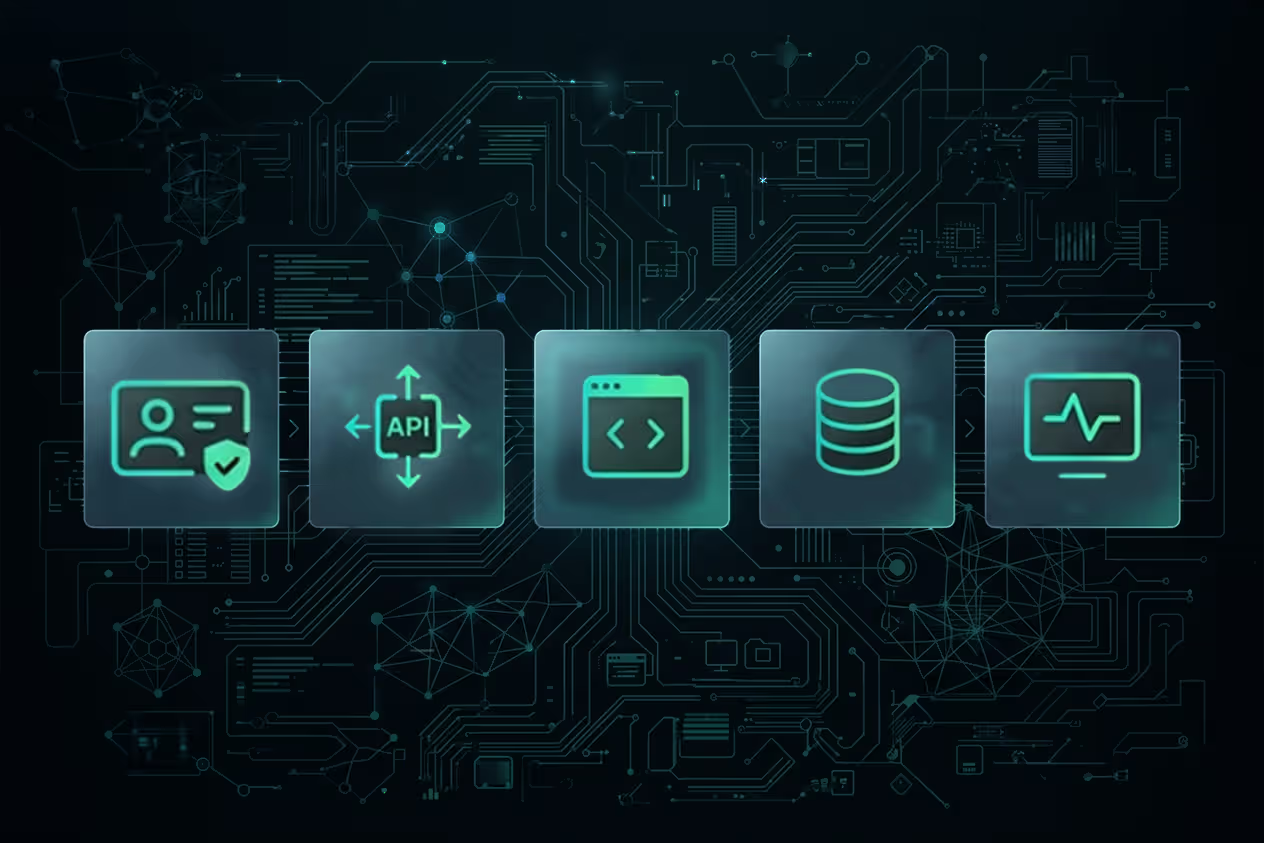
Identity, Authentication, and Access Controls

Build application access around clearly defined user identities, roles, permissions, and authentication requirements. Implement SSO integration, role-based access control (RBAC), session management, and privileged-access restrictions to protect sensitive functionality, and prevent unauthorized actions.

02

Secure APIs and Application Integrations

Protect the interfaces connecting your applications with enterprise systems, third-party platforms, and external services. Implement API authentication, authorization policies, secure data exchange, input validation, and controlled access to application resources.

Related capability:API Design & Integration
03

Data Protection and Privacy Controls

Protect sensitive business and customer information throughout its application lifecycle. Implement data classification, encryption in transit and at rest, secrets management, data minimization, and retention controls. Align application-level privacy measures with applicable regulatory requirements and organizational policies.

04

Vulnerability Assessment and Secure Code Remediation

Identify and address security weaknesses before they become production risks. Apply secure coding practices, coordinate static and dynamic application security testing (SAST and DAST), analyze software dependencies, and remediate identified vulnerabilities. Support VAPT findings with corrective changes and retesting.

05

DevOps and Secure Deployment Pipelines

Integrate security checks into application build and deployment workflows. Configure automated code, dependency, secret, container, and configuration scanning where supported. Strengthen container security, deployment controls, and release validation to identify risks earlier in the software delivery lifecycle.

06

Application Architecture and Security Modernization

Address architectural weaknesses that increase application security risks. Review legacy dependencies, tightly coupled components, outdated frameworks, and insecure interfaces. Apply targeted code remediation, framework upgrades, modularization, and architecture improvements without requiring an unnecessary full application rebuild.

LET’S BUILD BETTER

Address Security and Privacy Concerns Before They Become Release Blockers

Review the application architecture, data flows, identity model, and delivery pipeline to identify the controls that matter most.

FAQs

Find quick answers to the most common questions about our services, process, and solutions.

FAQs
Is VAPT included in every application project?

Security testing should be scoped according to application risk and client requirements. VAPT may be performed by FutureSoft or coordinated with an approved independent provider.

Can you help remediate findings from another security auditor?

Yes. FutureSoft can analyze findings, prioritize remediation, implement fixes, and support retesting.

Do you guarantee GDPR or DPDP compliance?

No single application vendor can guarantee organizational compliance. FutureSoft can engineer application controls that support applicable privacy requirements and documented client policies.

Can security checks run in CI/CD?

Yes, where the selected toolchain supports them. Code, dependency, secret, container, and configuration checks can be integrated as quality gates appropriate to the application.

Get Connected to FutureSoft

Stay Connected to Global Success